-
Cameroon Passive Fiber Optic Access Device gponont
GPON is an alternative to Ethernet switching in campus networking. GPON replaces the traditional three-tier Ethernet design with a two-tier optic network which eliminates access and distribution Etherne.
-
Application Access Switch Selection
If you are evaluating Cisco access switches for enterprise networks, start with five things: port density, PoE demand, uplink capacity, multigig requirements, growth planning, and fault isolation. Access switches are designed for cost-effectiveness and ease of use and provide the following features: ● High port diversity : Access switches offer a range of port types, such as 10/100/1000BASE-T ports, to accommodate the diverse access needs of various devices. The right Cisco access switch is the one that fits the wiring closet role and device mix over the next. This means the performance of the entire network relies on the data routed and switched by the core switch. It serves as a critical component of the access layer in a network's hierarchical design. Some switches have modulaqr chassis and others are fixed, like the 3750. So what criteria shoul done use to decide which would be the. This guide provides a comprehensive comparison of Access, Distribution, and Core switches, detailing their functions, characteristics, and deployment scenarios.
[PDF Version]
-
OLT is an access layer switch
The OLT is the core component of the optical access network, which is equivalent to a switch or router in a traditional communication network, and is also a multi-service providing platform. In short: The OLT (Optical Line Terminal) is the central control unit of a Passive Optical Network (PON). It converts data signals, manages bandwidth, and connects hundreds of users over a single optical fiber infrastructure. The shift from outdated electrical copper systems to optical fiber is driven by the immutable demands for. Central to the GPON system is the Optical Line Terminal (OLT), the core device responsible for aggregating data streams, managing Optical Network Terminal/Unit (ONT/ONU) devices, and performing application distribution and network management.
-
Reasons for the failure of the corridor access switch
Loose, frayed, or disconnected wires can lead to system failures. Check the configuration of the access control software. In many buildings, corridor lights, CCTV cameras, access control systems, motion sensors, intercom devices, and emergency signs may fail repeatedly even when the main power seems normal. Below is an overview of typical malfunctions and advice on how to identify and prevent them. The controller manages access authorization logic. The access control system is a modern security management system, which. Sometimes equipment will fail spontaneously for reasons such as chronological age, thermal age, state of chemical decomposition, state of contamination, and state of mechanical wear. Common solutions involve checking for physical damage, ensuring stable power supply.
-
Access Layer Switch Mode
These switches connect endpoints such as PCs, printers, VoIP phones, and wireless access points, enabling user traffic to enter the LAN. It includes the following topics: Access layer switches are primarily deployed in Layer 2 mode in the data center. What Is an Access Layer Switch? A Practical Guide for SMB Networks What Is the Access Layer Switch? In a typical enterprise network architecture, the access. When planning an enterprise access network, one of the most common dilemmas is whether to deploy Layer 2 (L2) or Layer 3 (L3) switches. It typically sits at the access layer, provides high port density, often delivers PoE, and forwards traffic. What is a Access Switch? The access switch is the network switch that connects the access layer with the subnets. FortiSwitch units distribute the ports to plugs.
-
Are access switches important
As key components in a network architecture, access switches are fundamental and widespread in hierarchical network design. An access switch is a network edge device that directly connects end-user hardware such as computers, IP phones, wireless access points, cameras, and IoT devices to the broader network. It typically sits at the access layer, provides high port density, often delivers PoE, and forwards traffic. In such high-capacity ethernet networks, switches are crucial as they direct data and transmit signals to the addressed devices. They enable communication, enforce traffic management, and play a vital role in maintaining efficient, secure data flow across an organization. It assists mainly in the switching of incoming and outgoing data packets to the right destination, as specified in MAC. The critical difference between a core, distribution, and access switch lies in its designated role within the three-tier network architecture.
[PDF Version]
-
Access Switch VLAN Configuration
Now, after separating the network into different VLANs, this means that we have created separate broadcast domains(one for each VLAN) and now hosts within the same VLAN can freely communicate between them (provided they bel. Now, after separating the network into different VLANs, this means that we have created separate broadcast domains(one for each VLAN) and now hosts within the same VLAN can freely communicate between them (provided they belong also in the same Layer 3 subnet). On the other hand, hosts that belong in different Layer 2 VLANs can't communicate between. Switch 1 Configuration: ! Create VLANs 2 and 4 in the switch database Switch1# configure terminal Switch1(config)# vlan 2 Switch1(config-vlan)# name Accounting Switch1(config-vlan)# end Switch1(config)# vlan 4 Switch1(config-vlan)# name Engineering Switch1(config-vlan)# end ! Assign Ports Fe0/1 and Fe0/2 in VLAN 2 Switch1(config)# interface fasteth. If you want to verify that the physical interfaces are assigned properly to each VLAN, then run the following show commands: SWITCH1#show vlan SWITCH2#show vlan.
[PDF Version]
-
Basic Access Speed of Switch
These include (1) Fast Ethernet switches (FS) – 10/100 Mbps (standard IEEE 802. Switching capacity, sometimes referred to as "backplane bandwidth," represents the total amount of data a switch can process through all of its ports at any given time. It's measured in gigabits per second (Gbps) or terabits per second (Tbps). Imagine a switch as a busy airport: the switching. When it comes to optimizing network performance, understanding the speed of a network switch is crucial. A network switch acts as a central hub for data transmission within a network, making it essential to comprehend its speed capabilities. The strategic design of a hierarchy network may comprise more than three layers. A switch is a discrete piece of hardware that connects various computers to a single local area network (LAN). It operates at the data link layer of the OSI model and ensures seamless communication between devices by forwarding data packets.
[PDF Version]
-
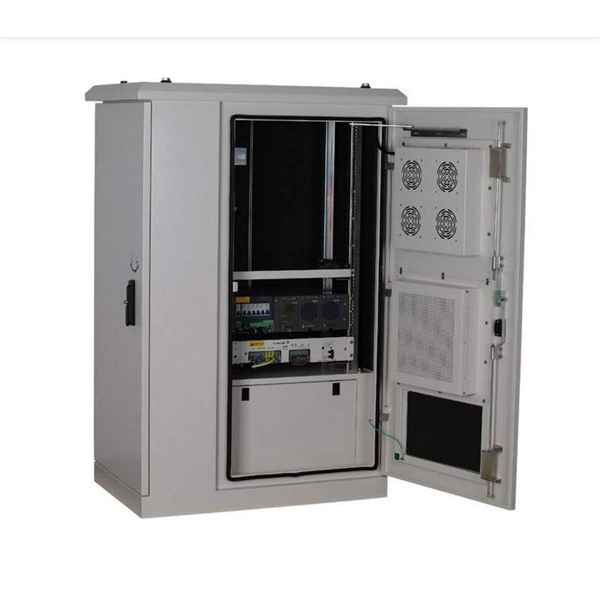
Monitoring system access switch
Switch port monitoring, along with autosensing capabilities, significantly improves the flexibility and reliability of a network, ensuring it runs smoothly while providing the necessary visibility for administrator.
-
200M Broadband Access Switch
Hardware DIP switch for “Standard” and “Extend” mode selection; the “Extend” mode features 30-watt PoE transmission distance of 200 meters at speed of 10Mbps. Port-based VLAN and Loop Protection features. TRENDnet's long-range PoE switches allow you to extend a PoE signal for up to 656 ft. TP-Link 5 Port Gigabit Outdoor Smart Ethernet Switch, Up to 200m PoE Network Splitter, 1-Port PoE++ In and 4-Port PoE+ Out, Weatherproof, Cloud Management (SG2005P-PD) Outdoor Weatherproof: IP55 waterproof, dustproof, and UV-resistant enclosure. Operation temperatures of -40 to 60 °C and 4KV. Up to 30W per PoE port for powering PoE-enabled devices. Auto-detection of powered devices (PD) and power consumption levels. Ideal for long-distance cameras and access points without speed loss* Eliminate mains access location limits and transmit data and power through one cable, simplifying installation. ETHERNET PORT CONFIGURATION: 8 Port Gigabit Long Range PoE+ Switch includes 8 Gigabit PoE+ ports provide a 16Gbps switching capacity to support edge network installations. Discover the capabilities of this intelligent tool that automates processes and adds intelligence to your network.
[PDF Version]
-
How to set up a fiber optic dynamic IP access router
To set up your router for fiber internet quickly, connect the router to your fiber modem, access the router's settings via a web browser, and input the provided ISP credentials. Make sure to update the firmware, configure Wi-Fi security, and customize your network name for. This FAQ article is designed to guide users in configuring the TP-Link Archer router. The internet connection type is usually one of the following three: Dynamic IP, Static IP, or PPPoE. As far as I understand, I need a PPPoE username and password to connect. I never received it from Telekom, as well as Access number (Zugangsnummer). Once logged in, navigate to the network settings section. Look for options related to WAN or.
-
RADIUS Authentication Access Switch
Configure the switch for RADIUS authentication through the following access methods: Console: Either direct serial-port connection or modem connection. Telnet: Inbound Telnet must be enabled (the default). SSH: To use RADIUS for SSH access, first configure the. RADIUS: RADIUS is a distributed client/server system that secures networks against unauthorized access by providing flexible administrative control over authentication, authorization processes, and offers detailed accounting information. These access policies are typically applied to ports on access-layer switches to prevent unauthorized devices. Home Knowledge Base Design & Configure How to configure RADIUS on Cisco switch (IOS) RADIUS is a security feature working in client/server mode. What's essential, RADIUS cannot control the. Juniper Networks Ethernet Switches use 802. This applies the privilege level specified by the service type value received from the RADIUS server.
[PDF Version]